
Tuesday, June 4, 2019


Tuesday, March 20, 2018
Rootkit Umbreon / Umreon - x86, ARM samples
 Pokémon-themed Umbreon Linux Rootkit Hits x86, ARM Systems
Research: Trend Micro
There are two packages
one is 'found in the wild' full and a set of hashes from Trend Micro (all but one file are already in the full package)
Wednesday, October 18, 2017
DDE Command Execution malware samples

Here are a few samples related to the recent DDE Command execution
 Download. Email me if you need the password (updated sample pack)
Friday, March 31, 2017
Part II. APT29 Russian APT including Fancy Bear

"APT29 - The Dukes Cozy Bear: APT29 is threat group that has been attributed to the Russian government and has operated since at least 2008.1210 This group reportedly compromised the Democratic National Committee starting in the summer of 2015" (src. Mitre ATT&CK)
Please see the first post here: Russian APT - APT28 collection of samples including OSX XAgent
Download (matching research listed above). Email me if you need the password Fancy_Bear_sourcecode (also on Github)Monday, March 20, 2017
DeepEnd Research: Analysis of Trump's secret server story
We posted our take on the Trump's server story. If you have any feedback or corrections, send me an email (see my blog profile on Contagio or DeepEnd Research)
Analysis of Trump's secret server story...

Monday, February 20, 2017
Part I. Russian APT - APT28 collection of samples including OSX XAgent

The post contains malware samples analyzed in the APT28 reports linked below. I will post APT29 and others later.
List of References (and samples mentioned) listed from oldest to newest:
- APT28_2011-09_Telus_Trojan.Win32.Sofacy.A
- APT28_2014-08_MhtMS12-27_Prevenity
- APT28_2014-10_Fireeye_A_Window_into_Russia_Cyber_Esp.Operations
- APT28_2014-10_Telus_Coreshell.A
- APT28_2014-10_TrendMicro Operation Pawn Storm. Using Decoys to Evade Detection
- APT28_2015-07_Digital Attack on German Parliament
- APT28_2015-07_ESET_Sednit_meet_Hacking
- APT28_2015-07_Telus_Trojan-Downloader.Win32.Sofacy.B
- APT28_2015-09_Root9_APT28_Technical_Followup
- APT28_2015-09_SFecure_Sofacy-recycles-carberp-and-metasploit-code
- APT28_2015-10_New Adobe Flash Zero-Day Used in Pawn Storm
- APT28_2015-10_Root9_APT28_targets Financial Markets
- APT28_2015-12_Bitdefender_In-depth_analysis_of_APT28–The_Political_Cyber-Espionage
- APT28_2015-12_Kaspersky_Sofacy APT hits high profile targets
- APT28_2015_06_Microsoft_Security_Intelligence_Report_V19
- APT28_2016-02_PaloAlto_Fysbis Sofacy Linux Backdoor
- APT29_2016-06_Crowdstrike_Bears in the Midst Intrusion into the Democratic National Committee << DNC (NOTE: this is APT29)
- APT28_2016-07_Invincea_Tunnel of Gov DNC Hack and the Russian XTunnel
- APT28_2016-10_ESET_Observing the Comings and Goings
- APT28_2016-10_ESET_Sednit A Mysterious Downloader
- APT28_2016-10_ESET_Sednit Approaching the Target
- APT28_2016-10_Sekoia_Rootkit analysisUse case on HideDRV
- APT28_2017-02_Bitdefender_OSX_XAgent << OSX XAgent
Download
Download sets (matching research listed above). Email me if you need the passwordDownload all files/folders listed (72MB)
Wednesday, August 24, 2016
Linux.Agent malware sample - data stealer

Research: SentinelOne, Tim Strazzere Hiding in plain sight?
Sample credit: Tim Strazzere
List of files
9f7ead4a7e9412225be540c30e04bf98dbd69f62b8910877f0f33057ca153b65 malware
d507119f6684c2d978129542f632346774fa2e96cf76fa77f377d130463e9c2c malware
fddb36800fbd0a9c9bfffb22ce7eacbccecd1c26b0d3fb3560da5e9ed97ec14c script.decompiled-pretty
ec5d4f90c91273b3794814be6b6257523d5300c28a492093e4fa1743291858dc script.decompiled-raw
4d46893167464852455fce9829d4f9fcf3cce171c6f1a9c70ee133f225444d37 script.dumped
malware_a3dad000efa7d14c236c8018ad110144
malware fcbfb234b912c84e052a4a393c516c78
script.decompiled-pretty aab8ea012eafddabcdeee115ecc0e9b5
script.decompiled-raw ae0ea319de60dae6d3e0e58265e0cfcc
script.dumped b30df2e63bd4f35a32f9ea9b23a6f9e7
Download
Download. Email me if you need the passwordWednesday, August 17, 2016
"i am lady" Linux.Lady trojan samples
Bitcoin mining malware for Linux servers - samples
 Research: Dr. Web. Linux.Lady
Sample Credit: Tim Strazzere
MD5 list:
0DE8BCA756744F7F2BDB732E3267C3F4
55952F4F41A184503C467141B6171BA7
86AC68E5B09D1C4B157193BB6CB34007
E2CACA9626ED93C3D137FDF494FDAE7C
E9423E072AD5A31A80A31FC1F525D614
Download. Email me if you need the password.
Sunday, March 6, 2016
Ransomware.OSX.KeRanger samples

Research: New OS X Ransomware KeRanger Infected Transmission BitTorrent Client Installer by Claud Xiao
Sample credit: Claud Xiao
File information
1d6297e2427f1d00a5b355d6d50809cb
Transmission-2.90.dmg
e3ad733cea9eba29e86610050c1a15592e6c77820927b9edeb77310975393574
56b1d956112b0b7bd3e44f20cf1f2c19
Transmission
31b6adb633cff2a0f34cefd2a218097f3a9a8176c9363cc70fe41fe02af810b9
14a4df1df622562b3bf5bc9a94e6a783
General.rtf
d7d765b1ddd235a57a2d13bd065f293a7469594c7e13ea7700e55501206a09b5
24a8f01cfdc4228b4fc9bb87fedf6eb7
Transmission2.90.dmg
ddc3dbee2a8ea9d8ed93f0843400653a89350612f2914868485476a847c6484a
3151d9a085d14508fa9f10d48afc7016
Transmission
6061a554f5997a43c91f49f8aaf40c80a3f547fc6187bee57cd5573641fcf153
861c3da2bbce6c09eda2709c8994f34c
General.rtf
Download
Tuesday, February 23, 2016
Files download information

It is harmful only if you harm your own pc and but not suitable for distribution or infecting unsuspecting users but I have not been able to resolve this with Google and Mediafire.
Mediafire suspended public access to Contagio account.
The file hosting will be moved.
If you need any files now, email me the posted Mediafire links (address in profile) and I will pull out the files and share via other methods.
P.S. I have not been able to resolve "yet" because it just happened today, not because they refuse to help. I don't want to affect Mediafire safety reputation and most likely will have to move out this time.
The main challenge is not to find hosting, it is not difficult and I can pay for it, but the effort move all files and fix the existing links on the Blogpost, and there are many. I planned to move out long time ago but did not have time for it. If anyone can suggest how to change all Blogspot links in bulk, I will be happy.
P.P.S. Feb. 24 - The files will be moved to a Dropbox Business account and shared from there (Dropbox team confirmed they can host it )
The transition will take some time, so email me links to what you need.
Thank you all
M
Wednesday, August 12, 2015
Potao Express samples
http://www.welivesecurity.com/2015/07/30/operation-potao-express/
http://www.welivesecurity.com/wp-content/uploads/2015/07/Operation-Potao-Express_final_v2.pdf
 TL; DR
http://www.welivesecurity.com/wp-content/uploads/2015/07/Operation-Potao-Express_final_v2.pdf
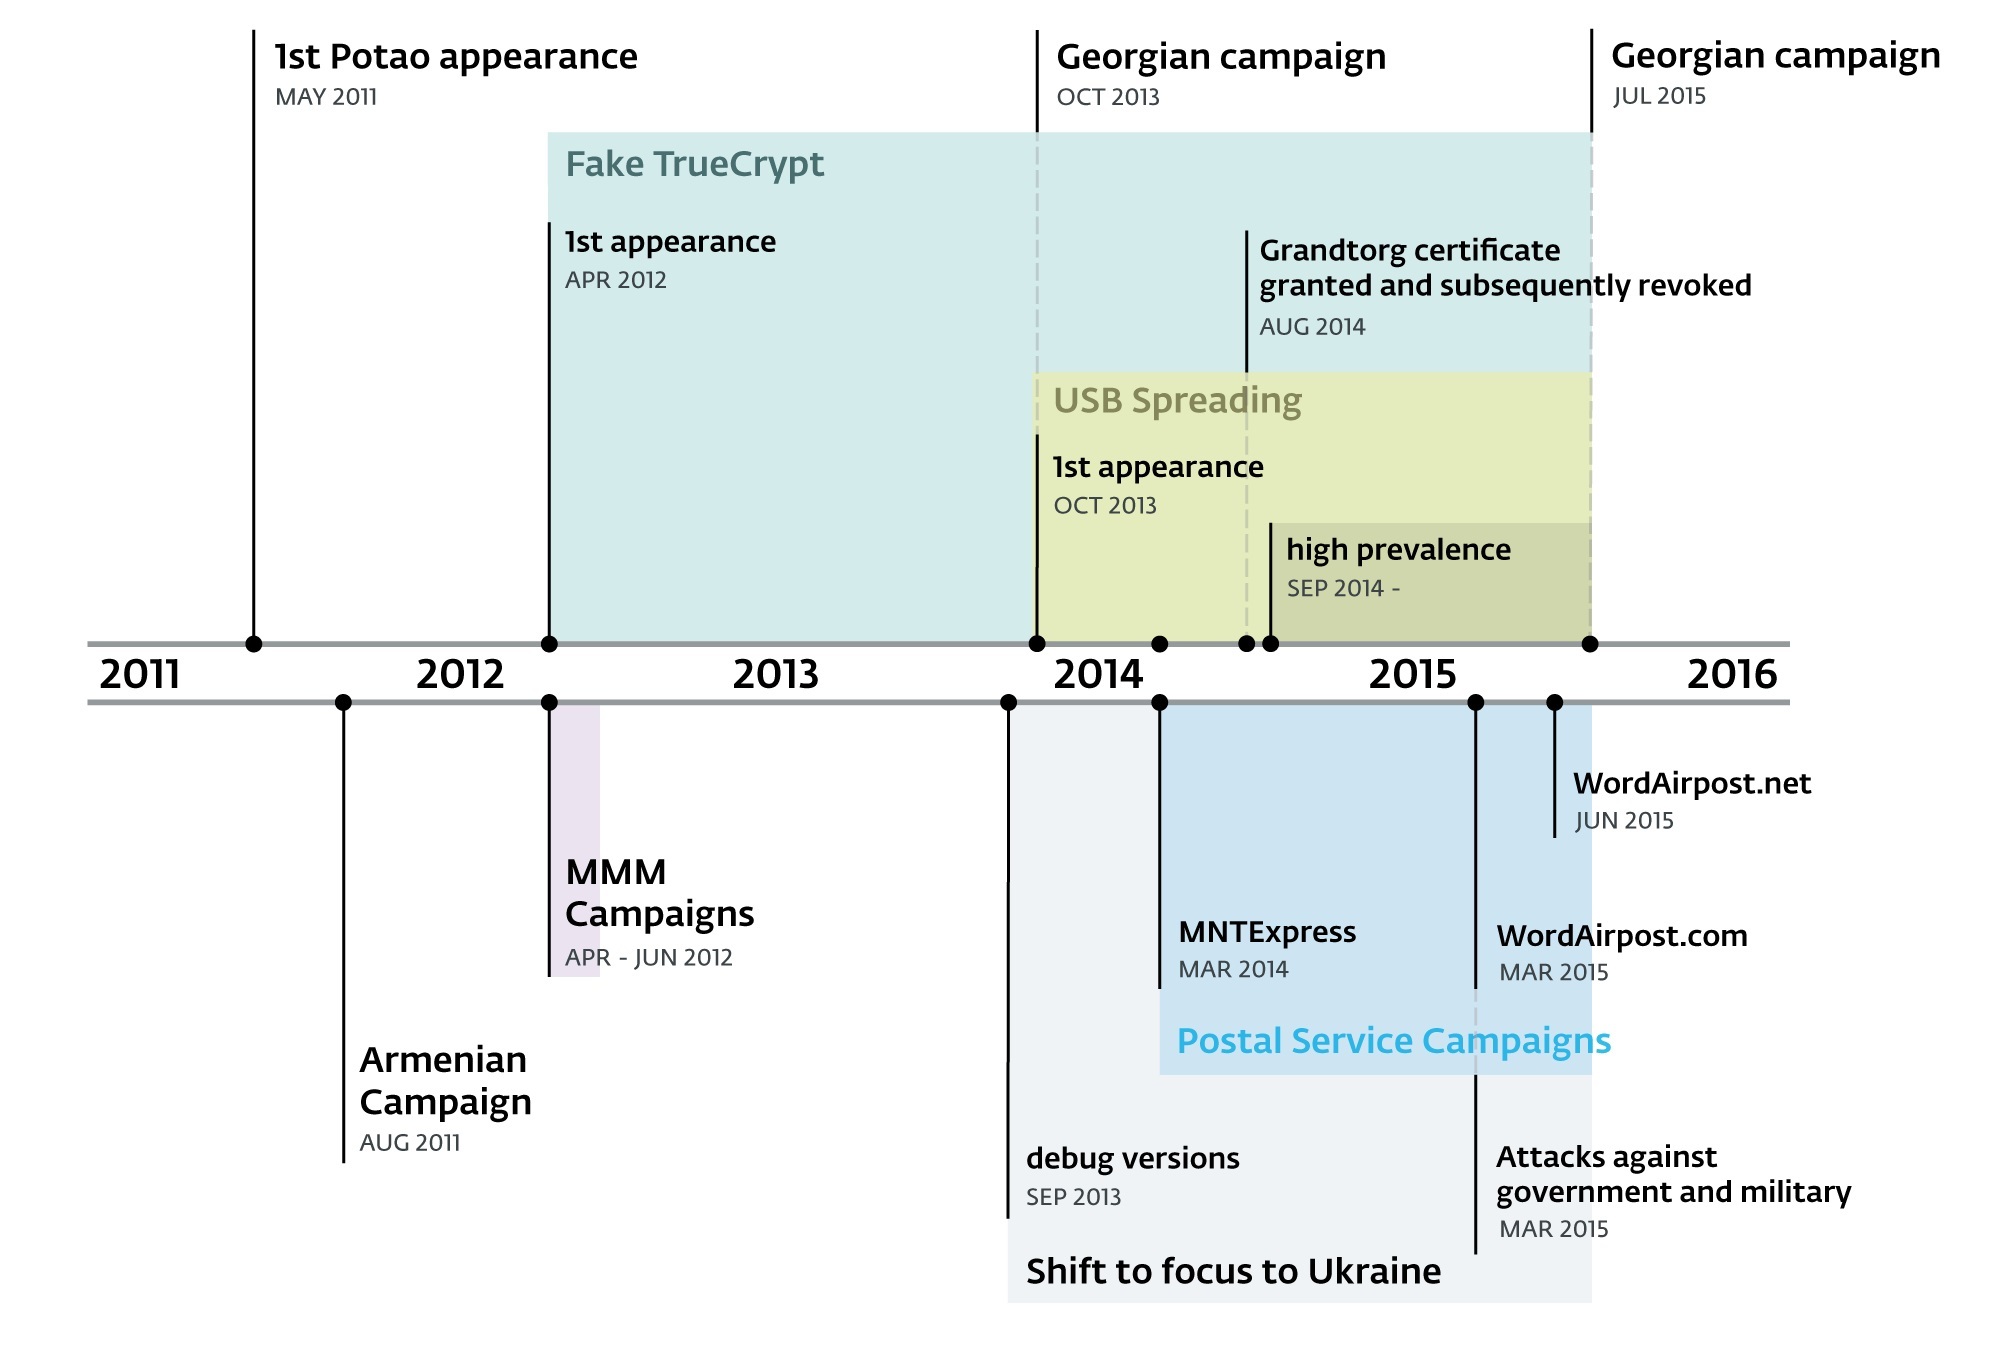
2011- July 2015
- Aka Sapotao and node69
- Group - Sandworm / Quedagh APT
- Vectors - USB, exe as doc, xls
- Victims - RU, BY, AM, GE
- Victims - MMM group, UA gov
- truecryptrussia.ru has been serving modified versions of the encryption software (Win32/FakeTC) that included a backdoor to selected targets.
- Win32/FakeTC - data theft from encrypted drives
- The Potao main DLL only takes care of its core functionality; the actual spying functions are implemented in the form of downloadable modules. The plugins are downloaded each time the malware starts, since they aren’t stored on the hard drive.
- 1st Full Plugin and its export function is called Plug. Full plugins run continuously until the infected system is restarted
- 2nd Light Plugin with an export function Scan. Light plugins terminate immediately after returning a buffer with the information they harvested off the victim’s machine.
- Some of the plugins were signed with a certificate issued to “Grandtorg”:
- Traffic
- Strong encryption. The data sent is encapsulated using the XML-RPC protocol.
- MethodName value 10a7d030-1a61-11e3-beea-001c42e2a08b is always present in Potao traffic.
- After receiving the request the C&C server generates an RSA-2048 public key and signs this generated key with another, static RSA-2048 private key .
- In 2nd stage the malware generates a symmetric AES-256 key. This AES session key is encrypted with the newly received RSA-2048 public key and sent to the C&C server.
- The actual data exchange after the key exchange is then encrypted using symmetric cryptography, which is faster, with the AES-256 key
- The Potao malware sends an encrypted request to the server with computer ID, campaign ID, OS version, version of malware, computer name, current privileges, OS architecture (64 or 32bits) and also the name of the current process.
- Potao USB - uses social engineering, exe in the root disguised as drive icon
- Potao Anti RE - uses the MurmurHash2 algorithm for computing the hashes of the API function names.
- Potao Anti RE - encryption of strings
- Russian TrueCrypt Win32/FakeTC - The malicious program code within the otherwise functional TrueCrypt software runs in its own thread. This thread, created at the end of the Mount function, enumerates files on the mounted encrypted drive, and if certain conditions are met, it connects to the C&C server, ready to execute commands from the attackers.
- IOC https://github.com/eset/malware-ioc/tree/master/potao
Tuesday, May 12, 2015
An Overview of Exploit Packs (Update 25) May 2015
Added CVE-2015-0359 and updates for CVE-2015-0336
Sunday, March 8, 2015
Ask and you shall receive
 |
Yes, I often obtain samples from various sources for my own research.
I am sometimes too lazy/busy to post them but don't mind sharing.
If you are looking for a particular sample, feel free to ask. I might have it.
Send MD5 (several or few samples). I cannot provide hundreds/thousands of samples or any kind of feeds. If you ask for a particular family, I might be able to help if I already have it.
Unfortunately, I do not have time to do homework for students and provide very specific sets for malware with specific features as well as guarantee the C2s are still active. Send your MD5(s) or at least malware family and I check if I have it :) If i have it, I will either send you or will post on the blog where you can download.
If you emailed me in the past and never got an answer, please remind me. Sometimes emails are long with many questions and I flag them to reply to later, when I have time and they get buried or I forget. It does not happen very often but accept my apologies if it happened to you.
Before you ask, check if it is already available via Contagio or Contagio Mobile.
1. Search the blog using the search box on the right side
2. Search here https://www.mediafire.com/folder/b8xxm22zrrqm4/BADINFECT
3. Search here https://www.mediafire.com/folder/c2az029ch6cke/TRAFFIC_PATTERNS_COLLECTION
4. Search here https://www.mediafire.com/folder/78npy8h7h0g9y/MOBILEMALWARE
Cheers, Mila
Sunday, January 4, 2015

Monday, November 17, 2014
AlienSpy Java RAT samples and traffic information


AlienSpy Java based cross platform RAT is another reincarnation of ever popular Unrecom/Adwind and Frutas RATs that have been circulating through 2014.
It appears to be used in the same campaigns as was Unrccom/Adwind - see the references. If C2 responds, the java RAT downloads Jar files containing Windows Pony/Ponik loader. The RAT is crossplatform and installs and beacons from OSX and Linux as well. However, it did not download any additional malware while running on OSX and Linux.
The samples, pcaps, and traffic protocol information are available below.
Saturday, November 15, 2014
OnionDuke samples

Download
File attributes
Size: 219136
MD5: 28F96A57FA5FF663926E9BAD51A1D0CB
Size: 126464
MD5: C8EB6040FD02D77660D19057A38FF769
Size: 316928
MD5: D1CE79089578DA2D41F1AD901F7B1014
Thursday, November 6, 2014
Wirelurker for OSX, iOS (Part I) and Windows (Part II) samples
PART II
 Wirelurker for Windows (WinLurker)
Research: Palo Alto Claud Xiao: Wirelurker for Windows
Sample credit: Claud Xiao
PART I
 Research: Palo Alto Claud Xiao WIRELURKER: A New Era in iOS and OS X Malware
Palo Alto |Claud Xiao - blog post Wirelurker
Wirelurker Detector https://github.com/PaloAltoNetworks-BD/WireLurkerDetector
Sample credit: Claud Xiao
Download
Download Part I
Download Part II
Email me if you need the password
Thursday, October 2, 2014
ShellShock payload sample Linux.Bashlet

Monday, July 21, 2014
CZ Solution Ltd. signed samples of Xtreme Rat, Zeus, Spy-Net, Gh0st, BozokRAT and other
 Here are all samples (+ more) mentioned in this post by Fireeye : The Little Signature That Could: The Curious Case of CZ Solution"
All files are digitally signed with a "CZ Solutions" certificate making it easy to create a Yara or ClamAV signature.
A few Zeus samples seem to be still beaconing. Most are sinkholed.
The certificate is now revoked by VeriSign.
Enjoy
Download
Friday, November 22, 2013
OSX malware and exploit collection (~100 files) + links and resources for OSX malware analysis

'Tis the season.
Here is a nice collection of ~100 Mac OS malware and Word document exploits carrying MacOS payload (all are CVE-2009-0563) along with links for OSX malware analysis.
Please send your favorite tools for OSX if they are not listed.
CVE-2009-0563
CVE-2009-0563Stack-based buffer overflow in Microsoft Office Word 2002 SP3, 2003 SP3, and 2007 SP1 and SP2; Microsoft Office for Mac 2004 and 2008; Open XML File Format Converter for Mac; Microsoft Office Word Viewer 2003 SP3; Microsoft Office Word Viewer; and Microsoft Office Compatibility Pack for Word, Excel, and PowerPoint 2007 File Formats SP1 and SP2 allows remote attackers to execute arbitrary code via a Word document with a crafted tag containing an invalid length field, aka "Word Buffer Overflow Vulnerability."
Links
Some OSX malware analysis tools and links
- http://computer-forensics.sans.org/community/papers/gcfa/mac-os-malware-analysis_2286
- http://en.wikibooks.org/wiki/Reverse_Engineering/Mac_OS_X
- http://contagiodump.blogspot.com/2012/12/osxdockstera-and-win32trojanagentaxmo.html
Tools
- Activity Monitor (Max OSX Utilities folder)
- MacMemoryze (support for Mountain Lion) free,
- Volatility (partial support for Mountain lion) free
- fseventer (graphical event representation) - works on Mountain lion
- Wireshark
- IDA pro
- OSXpmem (kernel extension)
- http://osxbook.com/ OSX internals
- 2009 Mac OS X Malware Analysis Author: Joel Yonts
- Apple OS X ABI Mach-O File Format Reference
- FileXray $79 but looks like it is worth it if you do OSX forensics
- ...let us know what you use
Malware in the provided package - links to research and news articles
- OSX_AoboKeylogger http://aobo.cc/
- OSX_BackTrack-A
- OSX_Boonana http://contagiodump.blogspot.com/2010/11/nov-14-javaboonana-facebook-trojan.html
- OSX_ChatZum http://www.thesafemac.com/chatzum-discovered-in-another-installer/
- OSX_Clapzok http://www.intego.com/mac-security-blog/clapzok-a-multi-platform-virus/
- OSX_Crisis http://www.intego.com/mac-security-blog/new-apple-mac-trojan-called-osxcrisis-discovered-by-intego-virus-team/
- OSX_Dockster_Backdoor http://contagiodump.blogspot.com/2012/12/osxdockstera-and-win32trojanagentaxmo.html
- OSX_FkCodec http://www.thesafemac.com/osxfkcodec-a-in-action/
- OSX_Flashback http://www.symantec.com/security_response/writeup.jsp?docid=2012-041001-0020-99
- OSX_Fucobha_IceFog http://www.securelist.com/en/blog/208214064/The_Icefog_APT_A_Tale_of_Cloak_and_Three_Daggers
- OSX_GetShell http://www.symantec.com/security_response/writeup.jsp?docid=2013-020412-3611-99
- OSX_Hacktool_Hoylecann
- OSX_HellRaiser http://macscan.securemac.com/hellraiser-aka-osxhellrtsd/
- OSX_HellRTS http://macscan.securemac.com/hellraiser-aka-osxhellrtsd/
- OSX_Hovdy_Backdoor http://www.sophos.com/en-us/threat-center/threat-analyses/viruses-and-spyware/OSX~Hovdy-A.aspx
- OSX_Inqtana http://www.symantec.com/security_response/writeup.jsp?docid=2006-021715-3051-99&tabid=2
- OSX_Iservice http://www.symantec.com/connect/blogs/osxiservice-it-s-not-going-iwork-you
- OSX_Jahlav http://macscan.securemac.com/osxjahlav-c-dnschanger-trojan-horse/
- OSX_Kitmos http://blog.sbarbeau.fr/2013/05/osx-kitmos-analysis.html
- OSX_Lamadai http://www.welivesecurity.com/2012/03/28/osxlamadai-a-the-mac-payload/
- OSX_Leverage_A_Backdoor http://www.alienvault.com/open-threat-exchange/blog/osx-leveragea-analysis
- OSX_LocalRoot https://www.trustedsec.com/august-2013/osx-10-8-4-local-root-privilege-escalation-exploit/
- OSX_Macarena_A http://www.securelist.com/en/analysis/204791948/Mac_OS_X#macarena
- OSX_MacDefender http://www.intego.com/mac-security-blog/macdefender-rogue-anti-malware-program-attacks-macs-via-seo-poisoning/
- OSX_MacKontrol http://www.securelist.com/en/blog/208193616/New_MacOS_X_backdoor_variant_used_in_APT_attacks
- OSX_Macsweeper http://en.securitylab.ru/viruses/311798.php
- OSX_Miner_DevilRobber http://www.sophos.com/en-us/threat-center/threat-analyses/viruses-and-spyware/OSX~Miner-D/detailed-analysis.aspx
- OSX_Olyx_Backdoor http://contagiodump.blogspot.com/2011/07/jul-25-mac-olyx-gh0st-backdoor-in-rar.html
- OSX_OpinionSpy http://www.f-secure.com/sw-desc/spyware_osx_opinionspy.shtml
- OSX_PSides
- OSX_Genieo http://www.thesafemac.com/malicious-genieo-installers-persist/
- OSX_PUP_PerfectKeylog http://www.blazingtools.com/mac_keylogger.html
- OSX_Renepo / Pintsized http://www.intego.com/mac-security-blog/pint-sized-backdoor-for-os-x-discovered/
- OSX_Revir http://contagiodump.blogspot.com/2012/11/group-photoszip-osxrevir-osximuler.html
- OSX_Safari
- OSX_SniperSpy http://www.sniperspymac.com/download.html
- OSX_Wirenet http://www.webroot.com/blog/2012/09/14/wirenet-the-password-stealing-trojan-lands-on-linux-and-os-x/
- OSX_Yontoo http://www.macrumors.com/2013/03/21/new-yontoo-adware-trojan-targets-major-browsers-on-os-x/
- OSXWeapoX http://www.virusradar.com/OSX_Rootkit.Weapox.A/description
- ------------------------------------
- CVE-2009-0563 Word exploit
- MacControl payload http://www.securelist.com/en/blog/208193616/New_MacOS_X_backdoor_variant_used_in_APT_attacks
- OSX.SabPub payload http://www.securelist.com/en/blog/208193470/New_Version_of_OSX_SabPub_Confirmed_Mac_APT_attacks
- OSX/Dockster.A payload http://www.intego.com/mac-security-blog/new-targeted-attack-on-tibetan-activists-using-os-x-discovered/
- OSX_Docklight payload http://contagioexchange.blogspot.com/2012/05/019-speechdoc-macosxms09-027a-word.html and http://blogs.technet.com/b/mmpc/archive/2012/04/30/an-interesting-case-of-mac-osx-malware.aspx
Friday, August 9, 2013
DeepEnd Research: List of malware pcaps, samples, and indicators for the Library of Malware Traffic Patterns

The library of malware traffic patterns have been popular. We found it very useful as well ourselves and we encourage you to send your contributions. I know at some point the spreadsheet will become unwieldy but I personally find it the most easy way (easy sort, search etc)
Currently, most of the samples described have the corresponding samples and pcaps available for download (email Mila @contagio for the password)
such as you see in the links below
Email us at mila [a t ] Deependresearch.org or adimino [a t] deependresearch.org
The current list of malware described (as of Aug. 9, 2013)
Wednesday, August 7, 2013
Defcon 21 Archives Speaker Materials
 Hope it is not a copyright violation and won't cause too much hate. I know Defcon will post better and complete data soon but many / most attendees did not receive the presentation CDs to their great sadness because there were not enough CDs available for all. Many authors and attendees published Defcon and Blackhat presentations online as well -you can track them via Twitter
You can download it here for now. Check Defcon website often, they will post it soon. The list of files of the speaker materials is below. The zip file also includes short stories. Please note that some presentations submitted for the DVD were somewhat / significantly different from what was presented. But better this than nothing, right?
SPEAKER MATERIALS - LIST OF PRESENTATIONS
Monday, June 10, 2013
REPRINT of http://contagiodump.blogspot.com/2013/09/sandbox-miming-cve-2012-0158-in-mhtml.html Sandbox MIMIng. CVE-2012-0158 in MHTML samples and analysis Unpublished May 27, 2024
 |
| Wikipedia |
I added more descriptions and changed NjRat / Backdoor.LV to Vidgrab - in the traffic communications are similar to NjRat/Backdoor;lv but it does not use base64 and sends initial request starting with ...3 (0x01 0x00 0x00 0x00 0x33) followed by null bytes - it does not start with lv|
I am still looking for names for a few other backdoors below, so if you recognize them, please let me know.
Recently, my custom sandbox has been trying to open some Word attachments in a browser because the filetype fingerprint service detected them as MIME HTML files. Browsers are usually the default applications for such types and they did contain the CVE-2012-0158 exploit. A quick Google lookup yielded a May 2013 report from the Chinese company Antiy "The Latest APT Attack by Exploiting CVE-2012-0158 Vulnerability", which described this new exploit vector.
Antiy noted that these MHTML files evade antivirus and indeed only half of vendors represented on Virustotal detect. However, many companies rely on their automated tools, inline and standalone sandboxes not just Antivirus to determine if the file is malicious.
I checked how these files (file without any extension) were processed by other commercial and open source mailboxes. 3 out of 5 well known commercial and open source mail scan and web sandbox vendors returned no output or informed me that that filetype was not supported. While writing this post, I noticed that Malwaretracker also mentioned the rise in this vector usage in his post on Friday, so I am sure the sandbox vendors are fixing the issue as we speak.
I checked 25 MHTML CVE-2012-0158 files and compared their targets (at least those I could obtain) and payload. The analysis showed a good variety of trojans and predominantly human rights (Tibet, Uyghur) activists. I will post a month worth of these files.
Saturday, June 1, 2013
DeepEnd Research: Under this rock... Vulnerable Wordpress/Joomla sites... Overview of the RFI botnet malware arsenal
 Exploits directed at Wordpress and/or Joomla content management systems(CMS) have been increasing at a dramatic rate over the past year. Internet blogs and forums are flooded with posts about hacked CMS installations. Popular jargon refers to the attackers as "hackers", but it is generally understood that these mass compromises are being performed via automated scanners and tools. However, we believe that there is not enough coverage of the actual malware involved.
One such infection scheme is essentially the following:
A downloader trojan (Mutopy - Win32) (20a6ebf61243b760dd65f897236b6ad3 Virustotal) instructs the infected host to download:
1) Remote File Injector "Symmi" (Win32) 7958f73daf4b84e3b00e008258ea2e7a Virustotal
2) SDbot (Win32) - aaee52bfb589f6534c4b51e3b144dc08 Virustotal
3) PHP scripts for injecting into compromised Wordpress sites. Among them a PHP spambot (victimized site owners often get alerted about copious amount of meds and spam porn emanating from their sites). This is also the source of varied links for spam using thousands of various links redirecting to the same sites (e.g. weightloss, work at home scams, or porn sites)
Download files (see below)
Subscribe to:
Posts (Atom)