
Wednesday, March 24, 2010

Mar 24 CVE-2010-0188 PDF rumours in N Korea2010march from coljoint@aol.com

Details 3fe225e4f42dad6a4c4863291f532dd2 rumours_in_N_Korea2010march.pdf
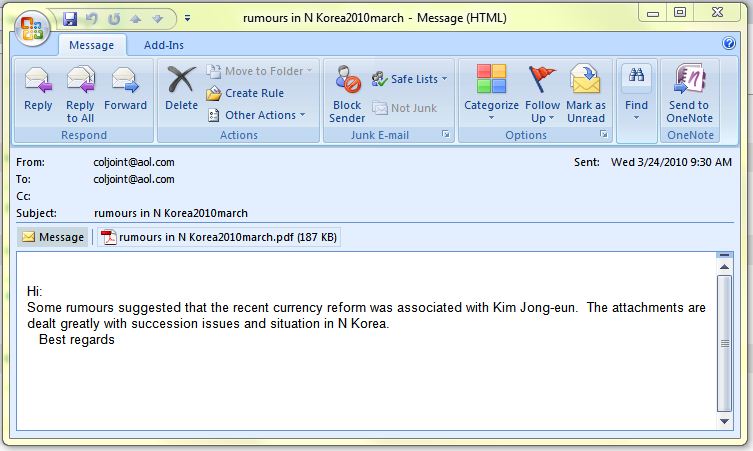
From: coljoint@aol.com [mailto:coljoint@aol.com]
Sent: Wednesday, March 24, 2010 9:30 AM
To: coljoint@aol.com
Subject: rumours in N Korea2010march
Importance: Low
Hi:
Some rumours suggested that the recent currency reform was associated with Kim Jong-eun. The attachments are dealt greatly with succession issues and situation in N Korea.
Best regards
File rumours_in_N_Korea2010march.pdf received on 2010.03.30 11:43:02 (UTC)Sent: Wednesday, March 24, 2010 9:30 AM
To: coljoint@aol.com
Subject: rumours in N Korea2010march
Importance: Low
Hi:
Some rumours suggested that the recent currency reform was associated with Kim Jong-eun. The attachments are dealt greatly with succession issues and situation in N Korea.
Best regards
http://www.virustotal.com/analisis/038c36b2f2f4404828a4c5881037d7be5e3373a4ab1ac2e8b2c49a021d22fcf0-1269949382
Result: 4/42 (9.53%)
ClamAV 0.96.0.0-git 2010.03.30 Exploit.PDF-17840
PCTools 7.0.3.5 2010.03.30 HeurEngine.Pdexe
Sophos 4.52.0 2010.03.30 Troj/PDFJs-II
Symantec 20091.2.0.41 2010.03.30 Trojan.Pidief.I
Additional information
File size: 191651 bytes
MD5...: 3fe225e4f42dad6a4c4863291f532dd2
parsed with pdf-parser.py
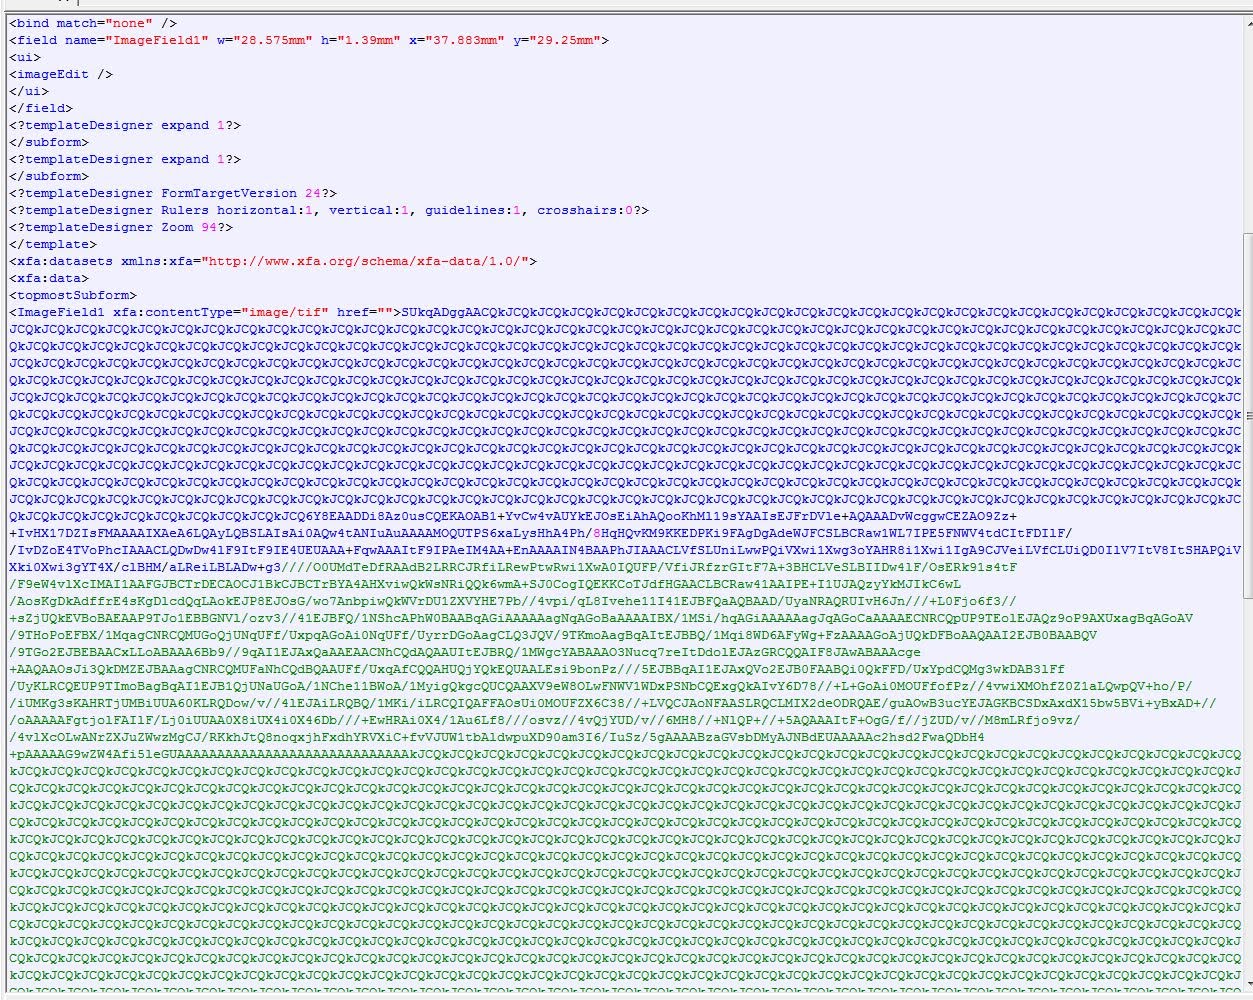

Mar 24 CVE--2010-0188 PDF My application from donald932@gmail.com


From: Huang [mailto:donald932@gmail.com]
Sent: Wednesday, March 24, 2010 4:26 AMTo: XXXXXXXXXXXX
Subject: : My application
This is my application, please check it appropriate or not, and
looking forward for your reply.
Huang
Virustotal
http://www.virustotal.com/analisis/dc29830cd35d8cf60df907c101daf05ad14111fa63c8071fd8f7465be2825968-1270006579
File application.PDF received on 2010.03.31 03:36:19 (UTC)
Result: 5/42 (11.91%)
ClamAV 0.96.0.0-git 2010.03.30 Exploit.PDF-17705
F-Secure 9.0.15370.0 2010.03.31 Exploit:W32/Pidief.CND
PCTools 7.0.3.5 2010.03.31 HeurEngine.Pdexe
Sophos 4.52.0 2010.03.31 Troj/PDFJs-II
Symantec 20091.2.0.41 2010.03.31 Trojan.Pidief.I
Additional information
File size: 57116 bytes
MD5...: 76f7e8dc68b364abfd893f0e9340fae8


%user%\Local Settings\Temp\application.PDF
%user%\Local Settings\Temp\temp.tmp
%user%\Local Settings\Temp\xxx.exe
%user%\Temp\~.exe
%user%\help.dll
http://www.virustotal.com/analisis/60505da8832dd0f0d737e9793c8240185e00a1b44ac5ef4383e0d86bf5d97d71-1270010048
File help.dll received on 2010.03.31 04:34:08 (UTC)
Result: 4/36 (11.11%)
DrWeb 5.0.2.03300 2010.03.31 Trojan.LydraSpy.origin
Panda 10.0.2.2 2010.03.30 Suspicious file
Sophos 4.52.0 2010.03.31 Sus/Behav-113
Symantec 20091.2.0.41 2010.03.31 Suspicious.Insight
File size: 101376 bytes
MD5 : e868c642ed4040f0e6752fe427084d3d
all other files and connections are like in this post Mar 25 CVE-2010-0188 PDF Re: conference memo from jesseandy2@gmail.com

Tuesday, March 23, 2010
Mar 23 CVE-2009-4324 PDF Talking Points on Chinese Currency from eaisecs@nus.edu.sg

Download 211b644de9ff2610f92f01a33fdc635b EAIBB_No._512.pdf as a password protected archive (please contact me for the password if you need it)
Details 211b644de9ff2610f92f01a33fdc635b EAIBB_No._512.pdf
Details 211b644de9ff2610f92f01a33fdc635b EAIBB_No._512.pdf

From: Yang Mu [mailto:eaisecs@nus.edu.sg]
Sent: Tuesday, March 23, 2010 8:29 AM
To: ;
Subject: Talking Points on Chinese Currency
Colleagues,
We are pleased to attach the following weekly talking points on Chinese Currency. This week's talking point centred on Premier Wen Jiabao's recent press conference.
Premier Wen criticised international pressure on China to appreciate its currency, calling it 'finger pointing'. China was accused of holding down the value of its currency. An undervalued currency keeps a country's exports inexpensive while making imports expensive.
Premier Wen's hardstand on not revaluating reminbi came as a surprise as it was only a few days before that Zhou Xiaochuan, the central banker, said at a press briefing that the country will allow the yuan to resume its appreciation at some point when it exits from the loose money and credit policies.
We hope you will find this report useful.
Yours sincerely,
Dr. Yang Mu
Co-ordinator, China Cooperation Programme
East Asian Institute
469A Bukit Timah Road
Tower Block #06-01
Singapore 259770
Tel: (65) 6516 3715
Fax: (65) 6779 3409
Email: eaisecs@nus.edu.sg
Headers
Received: from [204.12.252.250] (helo=3me8de026f8d12)by authsmtp01.yourhostingaccount.com with esmtpa (Exim)
id 1Nu3Eq-00017h-LJ; Tue, 23 Mar 2010 08:29:46 -0400
Message-ID:
From: "Yang Mu"
To:
Subject: Talking Points on Chinese Currency
Date: Tue, 23 Mar 2010 08:29:25 -0400
Hostname: 204.12.252.250
ISP: WholeSale Internet
Organization: Daigou Inc.
Country: United States
State/Region: Missouri
City: Kansas City

Monday, March 22, 2010
Mar 18 CVE-2009-4324 PDF Report on 2010 NPC Mar 18, 2010 8:53 AM


Sent: Thursday, March 18, 2010 8:53 AM
To: XXXXXXX
Subject: Report on 2010 NPC
Colleagues,
As you know, the National People’s Congress (NPC) is meeting in its annual plenary session in Beijing March 5 to 14, 2010. This year’s meeting, in addition to occurring on the heels of economic recession internationally, is also important as it marks the beginning of work on the new five year plan, China’s twelfth, which will take effect in 2011. This year ’s plenary session reviewed the Chinese government ’s work last year and discussed China’s social and economic priorities this year. This attached report highlights major policy discussion points expressed during the ten-day long meeting, looks at possible policy changes following the meeting as well as impacts on multinational companies, and includes recommendations for leveraging government priorities for business development.
I hope you find it interesting.
Best,
Ted
--
Ted Dean
Vice Chair- Board of Directors
AmCham-China
----------
Virustotal
http://www.virustotal.com/analisis/0d5d28212d31cd3871d17496420b3f2ac96856337b36bbf4412ebb77cec4751f-1269257719
File NPC_report.pdf received on 2010.03.22 11:35:19 (UTC)
Result: 10/42 (23.81%)
AhnLab-V3 5.0.0.2 2010.03.22 PDF/Exploit
Avast 4.8.1351.0 2010.03.21 JS:Pdfka-WP
Avast5 5.0.332.0 2010.03.21 JS:Pdfka-WP
BitDefender 7.2 2010.03.22 Exploit.PDF-JS.Gen
F-Secure 9.0.15370.0 2010.03.22 Exploit.PDF-JS.Gen
Kaspersky 7.0.0.125 2010.03.22 Exploit.JS.Pdfka.bvz
Microsoft 1.5605 2010.03.22 Exploit:Win32/Pdfjsc.CW
NOD32 4964 2010.03.22 JS/Exploit.Pdfka.NPK
nProtect 2009.1.8.0 2010.03.22 Exploit.PDF-JS.Gen
Additional information
File size: 235475 bytes
MD5...: ebec610267f0407a53021df441d1fd54
Wepawet
http://wepawet.cs.ucsb.edu/view.php?hash=ebec610267f0407a53021df441d1fd54&type=js
Jsand 1.02.02 malicious
doc.media.newPlayer Use-after-free vulnerability in the Doc.media.newPlayer method in Adobe Reader and Acrobat 8.0 through 9.2 CVE-2009-4324

Sunday, March 14, 2010
Mar 14 CVE-2010-0188 PDF 2010 Trade Policy Agenda from irc@state.gov

Sent: 2010-03-14 8:29 AM
To: XXXXXXXXXXXXXX
Subject: 2010 Trade Policy Agenda
2010 Trade Policy Agenda
Washington — President Obama, in his 2010 Trade Policy Agenda sent to Congress March 1, pledged the United States will build on existing trade agreements to strengthen the global trading system and uphold American values and commitments around the world.
The agenda items highlighted by USTR include the following:
*Support and strengthen a rules-based trading system. The United States strongly supports an ambitious and balanced Doha agreement that liberalizes three core market-access areas: agriculture, goods and services.
*Enforce rights in the rules-based trading system. USTR will strengthen further monitoring and enforcement, bringing cases at the World Trade Organization (WTO) as necessary, will increase focus on nontariff barriers that hinder exports, and will fully enforce labor and environmental rights in trade agreements.
*Enhance U.S. growth, job creation and innovation. The United States will emphasize bilateral relations with emerging markets as well as with long-standing key partners, and will pursue regional engagement, particularly negotiation of a Trans-Pacific Partnership Agreement to access key markets in the Asia-Pacific for decades to come.
*Work to resolve outstanding issues with pending free trade agreements (FTAs) and build on existing agreements. Proper resolution and implementation of the pending FTAs with Panama, Colombia and South Korea can bring significant economic benefits. In 2010, USTR will continue to consult with Congress and the public and to engage with these nations to address outstanding issues. It will also strengthen relationships with current partners such as Canada, Mexico, Japan and the European Union.
*Facilitate progress on national energy and environmental goals. Good trade policy can accelerate the success of sound energy and environmental initiatives and can complement sustainable growth. USTR will support fast-tracking action with willing partners in the WTO’s work on liberalizing trade in innovative, climate-friendly goods and services through tariff reductions and other initiatives.
*Foster stronger partnerships with developing and poor nations. The Obama administration supports expanding trade opportunities to stimulate market-led growth and help improve the lives of people in the least-developed nations. Opportunities created by open markets and preferences such as the Generalized System of Preferences require complementary measures such as technical assistance and market-based and rule-of-law reforms to maximize their benefits, USTR said.

Friday, March 12, 2010
Mar.12 CVE-2010-0188 Adobe PDF LibTiff Integer Overflow Code Execution Exploit Code by Villy
Title: Adobe PDF LibTiff Integer Overflow Code Execution.
Product: Adobe Acrobat ReaderAuthor: villy (villys777 at gmail.com)
CVE: 2010-0188
Site: http://bugix-security.blogspot.com/
Tested : successfully tested on Adobe Reader 9.1/9.2/9.3.0 OS Windows XP(SP2,SP3),
also works with Adobe browser plug-in
also works with Adobe browser plug-in
Exploit works with Adobe javascript disabled.
http://bugix-security.blogspot.com/2010/03/adobe-pdf-libtiff-working-exploitcve.htmlInvitation.pdf, the source sample
Update March 18, 2010
Excerpt:"This exploit worked flawlessly against Adobe Reader 9.3 despite DEP being enabled. (For those who didn't know, Adobe Reader 9 enables DEP "permanently".)
...
"What I found was that several function tails were being used to create a hunk memory of that was not protected by DEP. After this was created, a bit more ROP (return oriented proramming) was used to accomplish a "memcpy" of a small loader stub to this memory and execute it.
You might be asking yourself, "Great, but why do we care?" ... Well, AFAIK (feel free to comment), this is the first public exploit that uses multiple tail chunks to completely bypass permanent DEP. It certainly gives me a bit of chill to see this coming from a maliciously circulating document..." - More from blog.metasploit.com
Update March 17, 2010
Client Sides and Adobe 9.3 Excerpt:
A hacker by the nick of villy made a python script that will create a pdf that will launch calc.exe on a WinXP SP2 Box with the most up-to-date version of Adobe Reader installed even with Java turned off.
After playing with it we replaced the shellcode with a Windows Reverse Shell and then tried it on a fully patch system! BAM – Shell again.
We took the PDF file and uploaded it to Virus Total and an amazing 0/42 was returned and that is before we even used Shakata Ganai to encode it." - loganWHD
more from social-engineer.org
 Chris Hadnagy (aka loganWHD
) from www.social-engineer.org posted results of the exploit testing plus a video documenting their adventures.

Thursday, March 11, 2010
Mar 9. CVE-2010-0188 PDF+ exploit demo. Invitation.pdf- Formal invitation letter from sabrena66@yahoo.com.tw 2010-03-09
- CVE-2010-0188 Unspecified vulnerability in Adobe Reader and Acrobat 8.x before 8.2.1 and 9.x before 9.3.1 allows attackers to cause a denial of service (application crash) or possibly execute arbitrary code via unknown vectors
- Adobe Reader and The Unspecified Vulnerability from Secunia.com
- CVE-2010-0188 Adobe PDF LibTiff Integer Overflow Code Execution Exploit Code by Villy

Details 50b9bee0213917e52d32d82907234aeb invitation.pdf

CVE-2010-0188 - Adobe Pdf LibTiff Exploit (Remote Code Execution)

Sent: 2010-03-09 5:28 PM
To: XXX@sais-jhu.edu
Subject: formal invitation letter
attached is the copy of the formal invitation letter and response card.
Meanwhile We have send you the formal invitation letter by post
according to your correspondence address. Please check your mailbox in the
next few days.
Sincerely yours
Wang Xiaoxue
========================
CVE-2010-0188 Exploit
Here are a few details from Villy who reversed the file (thanks, Villy)
"The sample contains an embeded tiff file (with vulnerability CVE-2006-3459).
Possibly they used this code to generate the tiff file. The shellcode is in the tiff file.
http://downloads.
The following proof of concept video was created to show the exploit in action.
It was tested on Adobe Reader 9.0-9.3, on Windows XP, Vista, and Windows 7.
Windows XP with Adobe Reader 9.3.0 and below is vulnerable
Windows XP with Adobe Reader 9.3.1 is not vulnerable
Vista and Windows 7 are not vulnerable even with 9.3.0 - Adobe Reader just crashes but nothing else.
This exploit works with javascript disabled.For more details see his post at http://bugix-security.blogspot.com CVE-2010-0188 - Adobe Pdf LibTiff Exploit (Remote Code Execution)
====================
Received: from [60.216.233.216] by web72903.mail.tp2.yahoo.com via HTTP; Wed, 10 Mar 2010 06:27:34 CST
X-Mailer: YahooMailRC/300.3 YahooMailWebService/0.8.100.260964
Date: Wed, 10 Mar 2010 06:27:34 +0800
From: SABRENA
Reply-To: SABRENA
Subject: formal invitation letter
Hostname: 60.216.233.216
http://www.robtex.com/ip/60.216.233.216.html#whois
ISP: China Unicom Shandong province network
Organization: China Unicom Shandong province network
Country: China
State/Region: Shandong
City: Jinan
Virustotal result #1 - March 9, 2010
http://www.virustotal.com/analisis/feb8ee83587c61f4f53d2b0bcd39ca7c79666d1903c3dcdc53cbff94f0c90198-1268177735
File invitation.pdf received on 2010.03.09 23:35:35 (UTC)
Result: 0/42 (0.00%)
Virustotal result #2 -March 11, 2010
File invitation.pdf received on 2010.03.11 12:47:20 (UTC)
Current status: finished
File size: 225787 bytesCurrent status: finished
Result: 1/42 (2.38%)
Symantec 20091.2.0.41 2010.03.11 Trojan.Pidief.I
Symantec 20091.2.0.41 2010.03.11 Trojan.Pidief.I
MD5 : 50b9bee0213917e52d32d82907234aeb
=======================================================
This PDF appears to deliver Poison Ivy Remote Administration tool / backdoor type of malware
The following files get created on the exploited system
%System%\pe.dll
%System%\sens32.dll
%System%2\srvlic.dll
C:\data.bIN
C:\data.exe
%System%\pe.dll - injected in svchost process

Virustotal scans
%System%\pe.dll --5573689815aebfe7cbd2e3829054a5f0
%System%\sens32.dll --5573689815aebfe7cbd2e3829054a5f0
http://www.virustotal.com/analisis/25b0a8bb9c445e8ff2f93b37ad2792894ea1ef6b9dc5c89efd08a94cf9806bbb-1268343284
Result: 12/42 (28.58%)
AntiVir 8.2.1.180 2010.03.11 TR/Dldr.Agent.9216.5
BitDefender 7.2 2010.03.11 Trojan.Downloader.Agent.ZCR
eSafe 7.0.17.0 2010.03.11 Win32.Downloader.Age
F-Secure 9.0.15370.0 2010.03.11 Trojan.Downloader.Agent.ZCR
GData 19 2010.03.11 Trojan.Downloader.Agent.ZCR
McAfee 5917 2010.03.11 Generic BackDoor!cdn
McAfee+Artemis 5917 2010.03.11 Generic BackDoor!cdn
McAfee-GW-Edition 6.8.5 2010.03.11 Trojan.Dldr.Agent.9216.5
Microsoft 1.5502 2010.03.11 Backdoor:Win32/Poison.M
Panda 10.0.2.2 2010.03.11 Suspicious file
Rising 22.38.03.04 2010.03.11 Trojan.Win32.Generic.51FAA70A
Symantec 20091.2.0.41 2010.03.11 Suspicious.Insight
Additional information
File size: 9216 bytes
MD5...: 5573689815aebfe7cbd2e3829054a5f0
%System%2\srvlic.dll
http://www.virustotal.com/analisis/54962ca9c6c1815342d3bc47608ce5df997903aa53805f636361178f6b0a6c73-1268343232
Result: 1/42 (2.39%)
Symantec 20091.2.0.41 2010.03.11 Suspicious.Insight
File size: 3072 bytes
MD5...: 346754de64df87eb7709b168d04f8daf
C:\data.bIN
http://www.virustotal.com/analisis/d6c3a05e39ff7d48e77adec5a1fad0fca1b256a171b4d863bd34884345a087d3-1268343177
Result: 0/42 (0%)
File size: 91756 bytes
MD5...: 3c924ce0fc74b39d04822f4d26640311
C:\data.exe
http://www.virustotal.com/analisis/1b0d5103e2f621870f407bec6310069044f890a1f2a215468b09eb8182647016-1268342979
File data.EXE received on 2010.03.11 21:29:39 (UTC)
Result: 5/41 (12.2%)
McAfee+Artemis 5917 2010.03.11 Artemis!8557321BF6EC
McAfee-GW-Edition 6.8.5 2010.03.11 Heuristic.BehavesLike.Win32.CodeInjection.L
Rising 22.38.03.04 2010.03.11 Trojan.Win32.Generic.51FAA6DF
Sunbelt 5827 2010.03.11 Trojan.Win32.Generic!SB.0
Symantec 20091.2.0.41 2010.03.11 Suspicious.Insight
File size: 32768 bytes
MD5...: 8557321bf6ec39b0cb4ac9a9441d0487
TCP traffic - 202.59.152.123:443

Information from Robtex.com 202.59.152.123

Hostname: idc-123-152-59-202.hkt.cc
ISP: First Network Communications Limited, ISP at HK
Organization: First Network Communications Limited, ISP at HK
Country: Hong Kong
City: Central District
Some screenshots
Displayed PDF - note data.bIN as the name


Whois
http://www.robtex.com/ip/202.59.152.123.html#whois
inetnum: 202.59.152.0 - 202.59.159.255
netname: NET-FTG
descr: Forewin Telecom Group Limited
descr: ISP at HK
country: HK
admin-c: LC873-AP
tech-c: LC846-AP
status: ALLOCATED PORTABLE
mnt-by: APNIC-HM
mnt-lower: MAINT-HK-FTG
mnt-routes: MAINT-HK-FTG
remarks: -+-+-+-+-+-+-+-+-+-+-+-++-+-+-+-+-+-+-+-+-+-+-+-+-+-+
remarks: This object can only be updated by APNIC hostmasters.
remarks: To update this object, please contact APNIC
remarks: hostmasters and include your organisation's account
remarks: name in the subject line.
remarks: -+-+-+-+-+-+-+-+-+-+-+-++-+-+-+-+-+-+-+-+-+-+-+-+-+-+
changed: hm-changed@apnic.net 20060712
changed: hm-changed@apnic.net 20060901
changed: hm-changed@apnic.net 20070222
changed: hm-changed@apnic.net 20091020
source: APNIC
route: 202.59.152.0/21
descr: Forewin Telecom Group Limited, ISP at HK
origin: AS38186
mnt-by: MAINT-HK-FTG
changed: hostmaster@hkt.cc 20090306
source: APNIC
person: Edward Poon
nic-hdl: LC873-AP
e-mail: edward@hkt.cc
address: RM 6A, 25/F, Cable TV Tower
address: 9 Hoi Shing RD, Tsuen Wan
address: N.T. Hong Kong
address:
address: + Please send spam and abuse reports to
address: + < abuse@hkt.cc >
address:
phone: +852-23631363
fax-no: +852-81673882
country: HK
changed: hostmaster@hkt.cc 20091012
mnt-by: MAINT-HK-FTG
source: APNIC
person: Larry Chan
nic-hdl: LC846-AP
e-mail: ckchan@hkt.cc
address: RM 6A, 25/F, Cable TV Tower
address: 9 Hoi Shing RD, Tsuen Wan
address: N.T. Hong Kong
address:
address: + Please send spam and abuse reports to
address: + < abuse@hkt.cc >
address:
phone: +852-23631363
fax-no: +852-81673882
country: HK
changed: hostmaster@hkt.cc 20091012
mnt-by: MAINT-HK-FTG
source: APNIC

Wednesday, March 10, 2010
Mar 10 CVE-2010-0188 PDF Please take note - from plwang@gmail.com
- CVE-2010-0188 Unspecified vulnerability in Adobe Reader and Acrobat 8.x before 8.2.1 and 9.x before 9.3.1 allows attackers to cause a denial of service (application crash) or possibly execute arbitrary code via unknown vectors
- Adobe Reader and The Unspecified Vulnerability from Secunia.com
Expect code is this file to be different (and less reliable) from code in invitation.pdf described in Mar 9. CVE-2010-0188 PDF+ exploit demo. Formal invitation letter ...
Details [].pdf bbdce0ad4cd7268f8454b7da526aa09c

From: plwang@gmail.com [mailto:plwang@gmail.com]
Sent: Wednesday, March 10, 2010 10:08 PM
Subject: FW: 請收悉
請收悉
Sent: Wednesday, March 10, 2010 10:08 PM
Subject: FW: 請收悉
請收悉
From: plwang@gmail.com [mailto: plwang@gmail.com]Sent: Wednesday, March 10, 2010 10:08 PMSubject: FW: Please take note
Please acknowledge receipt
Virustotal
http://www.virustotal.com/analisis/da9ded47b77c9579016b11c8af195d99f17ede92ee67c40a01f9c2a3a12d3182-1268311477
File __.pdf received on 2010.03.11 12:44:37 (UTC)
Result: 6/41 (14.63%)
AhnLab-V3 5.0.0.2 2010.03.11 PDF/Cve-2010-0188
AVG 9.0.0.787 2010.03.11 Exploit_c.DEY
eSafe 7.0.17.0 2010.03.10 PDF.Exploit
Kaspersky 7.0.0.125 2010.03.11 Exploit.JS.Pdfka.bui
Microsoft 1.5502 2010.03.11 Exploit:Win32/Pidief.AY
Additional information
File size: 240872 bytes
MD5 : bbdce0ad4cd7268f8454b7da526aa09c
Wepawet cannot deal with CVE-2010-0188 - benign

Mar 10 CVE-2010-0188 PDF March Luncheon Invitation_FINAL from ikhtnamzels@yahoo.com
- CVE-2010-0188 Unspecified vulnerability in Adobe Reader and Acrobat 8.x before 8.2.1 and 9.x before 9.3.1 allows attackers to cause a denial of service (application crash) or possibly execute arbitrary code via unknown vectors
- Adobe Reader and The Unspecified Vulnerability from Secunia.com
Expect code is this file to be different from code in invitation.pdf described in Mar 9. CVE-2010-0188 PDF+ exploit demo. Formal invitation letter ...
Download 1a8a44c122449cf586419cfc5d6f36093e175037 2010 March Luncheon Invitation_FINAL.pdf as a password protected archive (please contact me if you need the password)
Details 2010_March_Luncheon_Invitation_FINAL.pdf 3639f34ad463932ab8ebad3e57421a97
Details 2010_March_Luncheon_Invitation_FINAL.pdf 3639f34ad463932ab8ebad3e57421a97

Sent: Wednesday, March 10, 2010 5:34 AM
To: MKoehler-Vice President Office Marc
Subject: 2010 March Luncheon Invitation_FINAL
attached is the copy of the formal invitation letter and response card.
Meanwhile We have send you the formal invitation letter by post
according to your correspondence address. Please check your mailbox in the
next few days.
Sincerely yours
Isidore
Virustotal scans - see dynamics from 0 to 8 over the course of 7 days
March 10
Result: 0/42 (0.00%)http://www.virustotal.com/analisis/3f327ecde65a536e9f197929ecb397dda92087cef2f563573104488ea5b7a923-1268219156
March 11
http://www.virustotal.com/analisis/3f327ecde65a536e9f197929ecb397dda92087cef2f563573104488ea5b7a923-1268311817 File 2010_March_Luncheon_Invitation_FI received on 2010.03.11 12:50:17 (UTC)
Result: 1/42 (2.38%)
Symantec 20091.2.0.41 2010.03.11 Trojan.Pidief.I
File size: 162579 bytes
MD5 : 3639f34ad463932ab8ebad3e57421a97
SHA1 : 1a8a44c122449cf586419cfc5d6f36093e175037
Update: March 17
http://www.virustotal.com/analisis/3f327ecde65a536e9f197929ecb397dda92087cef2f563573104488ea5b7a923-1268854486File 2010_March_Luncheon_Invitation_FI received on 2010.03.17 08:04:19 (UTC)
Result: 8/42 (19.05%)
AhnLab-V3 5.0.0.2 2010.03.16 PDF/Exploit
AntiVir 8.2.1.180 2010.03.16 EXP/Pidief.dbj
eTrust-Vet 35.2.7368 2010.03.17 PDF/Pidief.PU
Kaspersky 7.0.0.125 2010.03.17 Exploit.Win32.Pidief.dbi
McAfee-GW-Edition 6.8.5 2010.03.16 Exploit.Pidief.dbj
Microsoft 1.5605 2010.03.17 Exploit:Win32/Pdfjsc.gen!B
Sophos 4.51.0 2010.03.17 Troj/PDFJs-II
Symantec 20091.2.0.41 2010.03.17 Trojan.Pidief.I
File size: 162579 bytes
MD5 : 3639f34ad463932ab8ebad3e57421a97
Relevant Header info
Received: from [222.122.12.31] by web114207.mail.gq1.yahoo.com via HTTP; Wed, 10 Mar 2010 02:34:05 PSTX-Mailer: YahooMailRC/300.3 YahooMailWebService/0.8.100.260964
Robtex.com
Summary
Hostname: 222.122.12.31
ISP: Korea Telecom
Organization: Korea Telecom
Country: Korea, Republic of
State/Region: Soul-t'ukpyolsi
City: Seoul
ISP: Korea Telecom
Organization: Korea Telecom
Country: Korea, Republic of
State/Region: Soul-t'ukpyolsi
City: Seoul
Neeraj from Hypersecurity blog made an analysis of this sample -
CVE-2010-0188 Adobe Reader TIFF vulnerability


Mar 10 Energizer DUO USB Battery Charger trojan
Back Door Found in Energizer DUO USB Battery Charger Software - Symantec Security Response
US Cert Vulnerability Note


US Cert Vulnerability Note
- Download 3f4f10b927677e45a495d0cdd4390aaf UsbCharger_setup_V1_1_1_3_.exe as a password protected archive. Please contact me if you need the password
- Download the manual here (no password needed)
Details 3f4f10b927677e45a495d0cdd4390aaf UsbCharger_setup_V1_1_1_3_.exe


Tuesday, March 9, 2010
Mar 8 Trojan Win32.Magania from www71625@yahoo.com.tw
The message contains a password protected rar archive with

Result: 15/42 (35.72%)
AntiVir 8.2.1.180 2010.03.05 TR/Drop.Agen.283856
AVG 9.0.0.787 2010.03.07 PSW.OnlineGames3.AEQN
DrWeb 5.0.1.12222 2010.03.07 Trojan.Packed.1132
F-Secure 9.0.15370.0 2010.03.07 Trojan:W32/Agent.NRR
Fortinet 4.0.14.0 2010.03.07 SPY/Magania
Ikarus T3.1.1.80.0 2010.03.07 Worm.Win32.Taterf
Kaspersky 7.0.0.125 2010.03.07 Trojan-GameThief.Win32.Magania.cxsb
McAfee 5912 2010.03.06 New Malware.bl
McAfee+Artemis 5912 2010.03.06 New Malware.bl
McAfee-GW-Edition 6.8.5 2010.03.07 Trojan.Drop.Agen.283856
Microsoft 1.5502 2010.03.07 VirTool:Win32/Obfuscator.EX
Panda 10.0.2.2 2010.03.07 Trj/CI.A
Sophos 4.51.0 2010.03.07 Sus/UnkPack-C
Sunbelt 5780 2010.03.07 VirTool.Win32.Obfuscator
Symantec 20091.2.0.41 2010.03.07 Backdoor.Graybird
Additional information
File size: 284694 bytes
MD5...: d84c9278af1c162aff8ba617b56ba645

第一乞丐潮哥.cmd Size: 284694 MD5: D84C9278AF1C162AFF8BA617B56BA645 inside.
- Download 第一乞丐潮哥.cmd as a password protected archive (please contact me if you need the password).
- Download dropped files as a password protected archive (please contact me if you need the password).


From: www71625 [mailto:www71625@yahoo.com.tw]
Sent: Monday, March 08, 2010 6:53 PM
To: XXXXX
Subject: 超牛B,中國第一极品帥哥的傳說,蓋過現實明星..壓縮密碼668
咋樣?哥老犀利、老有型了,网絡從沒寂寞過。也不甘寂寞--..壓縮密碼668
AntiVir 8.2.1.180 2010.03.05 TR/Drop.Agen.283856
AVG 9.0.0.787 2010.03.07 PSW.OnlineGames3.AEQN
DrWeb 5.0.1.12222 2010.03.07 Trojan.Packed.1132
F-Secure 9.0.15370.0 2010.03.07 Trojan:W32/Agent.NRR
Fortinet 4.0.14.0 2010.03.07 SPY/Magania
Ikarus T3.1.1.80.0 2010.03.07 Worm.Win32.Taterf
Kaspersky 7.0.0.125 2010.03.07 Trojan-GameThief.Win32.Magania.cxsb
McAfee 5912 2010.03.06 New Malware.bl
McAfee+Artemis 5912 2010.03.06 New Malware.bl
McAfee-GW-Edition 6.8.5 2010.03.07 Trojan.Drop.Agen.283856
Microsoft 1.5502 2010.03.07 VirTool:Win32/Obfuscator.EX
Panda 10.0.2.2 2010.03.07 Trj/CI.A
Sophos 4.51.0 2010.03.07 Sus/UnkPack-C
Sunbelt 5780 2010.03.07 VirTool.Win32.Obfuscator
Symantec 20091.2.0.41 2010.03.07 Backdoor.Graybird
Additional information
File size: 284694 bytes
MD5...: d84c9278af1c162aff8ba617b56ba645
Symantec and PCtools detect it as Graybird, aka Gray Pigeon, but it is not. It is a classic Magania trojan described here by F- Secure

Monday, March 8, 2010
Mar 8 CVE-2010-0188 PDF China to participate in cross-strait relations seminar from spoofed titx@oa.tku.edu.tw
- CVE-2010-0188 Unspecified vulnerability in Adobe Reader and Acrobat 8.x before 8.2.1 and 9.x before 9.3.1 allows attackers to cause a denial of service (application crash) or possibly execute arbitrary code via unknown vectors
- Adobe Reader and The Unspecified Vulnerability from Secunia.com

From: 國際事務與戰略研究所 [mailto:titx@oa.tku.edu.tw]
Sent: Monday, March 08, 2010 8:54 PM
To: XXXXX
Subject: 敬邀參加兩岸關系研討會
From: International Affairs and Strategic Studies
[mailto: titx@oa.tku.edu.tw]Sent:
Monday, March 08, 2010 8:54 PMTo: XXXXXSubject: China to participate in cross-strait
relations seminar
Received: from IBM-62979760B13 ([211.75.147.173])
by msr39.hinet.net (8.9.3/8.9.3) with ESMTP id JAA10998
for XXXXXXXXXXX Tue, 9 Mar 2010 09:53:32 +0800 (CST)
Reply-To: titx@oa.tku.edu.tw
From: "=?BIG5?B?sOq72qjGsMi7UL7UsqSs46hzqdI=?="
Hostname: mx3.imedia.com.tw
ISP: CHTD, Chunghwa Telecom Co., Ltd.
Organization: Ming Siang Printing Co., Ltd.
Country: Taiwan
State/Region: T'ai-pei
City: Taipei
Virustotal scans
Scan 1
File _.pdf received on 2010.03.09 16:54:40 (UTC)
http://www.virustotal.com/analisis/be7578591f45418541d1e38b9389b3e35063a1cd61c1db489bac08e944bce258-1268153680
Result: 5/42 (11.90%)
eSafe 7.0.17.0 2010.03.09 PDF.Exploit
McAfee 5914 2010.03.08 Exploit-PDF.q.gen!stream
McAfee+Artemis 5915 2010.03.09 Exploit-PDF.q.gen!stream
Microsoft 1.5502 2010.03.09 Exploit:Win32/Pidief.AY
Additional information
File size: 80199 bytes
MD5 : cdb5e82e4d07911f9add5cdcf817e9ed
Scan 2
http://www.virustotal.com/analisis/be7578591f45418541d1e38b9389b3e35063a1cd61c1db489bac08e944bce258-1269343175
File _.pdf received on 2010.03.23 11:19:35 (UTC)
Result: 24/42 (57.15%)
a-squared 4.5.0.50 2010.03.23 Exploit.JS.Pdfka!IK
AhnLab-V3 5.0.0.2 2010.03.23 PDF/Cve-2010-0188
AntiVir 8.2.1.196 2010.03.23 EXP/Pidief.bui
Antiy-AVL 2.0.3.7 2010.03.23 Exploit/JS.Pdfka
Authentium 5.2.0.5 2010.03.23 JS/ShellCode.AM
AVG 9.0.0.787 2010.03.23 Exploit_c.DEY
BitDefender 7.2 2010.03.23 Exploit.PDF-EXE.Gen
DrWeb 5.0.1.12222 2010.03.23 Exploit.PDF.758
eSafe 7.0.17.0 2010.03.21 PDF.Exploit
eTrust-Vet 35.2.7383 2010.03.23 PDF/Pidief.PR
F-Secure 9.0.15370.0 2010.03.23 Exploit.PDF-EXE.Gen
GData 19 2010.03.23 Exploit.PDF-EXE.Gen
Ikarus T3.1.1.80.0 2010.03.23 Exploit.JS.Pdfka
Kaspersky 7.0.0.125 2010.03.23 Exploit.JS.Pdfka.bui
McAfee 5928 2010.03.22 Exploit-PDF.by
McAfee+Artemis 5928 2010.03.22 Exploit-PDF.by
McAfee-GW-Edition 6.8.5 2010.03.23 Exploit.Pidief.bui
Microsoft 1.5605 2010.03.23 Exploit:Win32/Pdfjsc.gen!B
Rising 22.40.01.04 2010.03.23 Hack.Exploit.PDF.aem
Sophos 4.51.0 2010.03.23 Troj/PDFJs-II
Sunbelt 6031 2010.03.22 Exploit.PDF.CVE-2010-0806 (v) - nope, it is not (M)
Symantec 20091.2.0.41 2010.03.23 Trojan.Pidief.I
TrendMicro 9.120.0.1004 2010.03.23 TROJ_PDFKA.AR
VirusBuster 5.0.27.0 2010.03.22 JS.Crypt.UQBF
Additional information
File size: 80199 bytes
MD5...: cdb5e82e4d07911f9add5cdcf817e9ed
Wepawet
benign
http://wepawet.cs.ucsb.edu/view.php?hash=cdb5e82e4d07911f9add5cdcf817e9ed&type=js
Subscribe to:
Posts (Atom)